

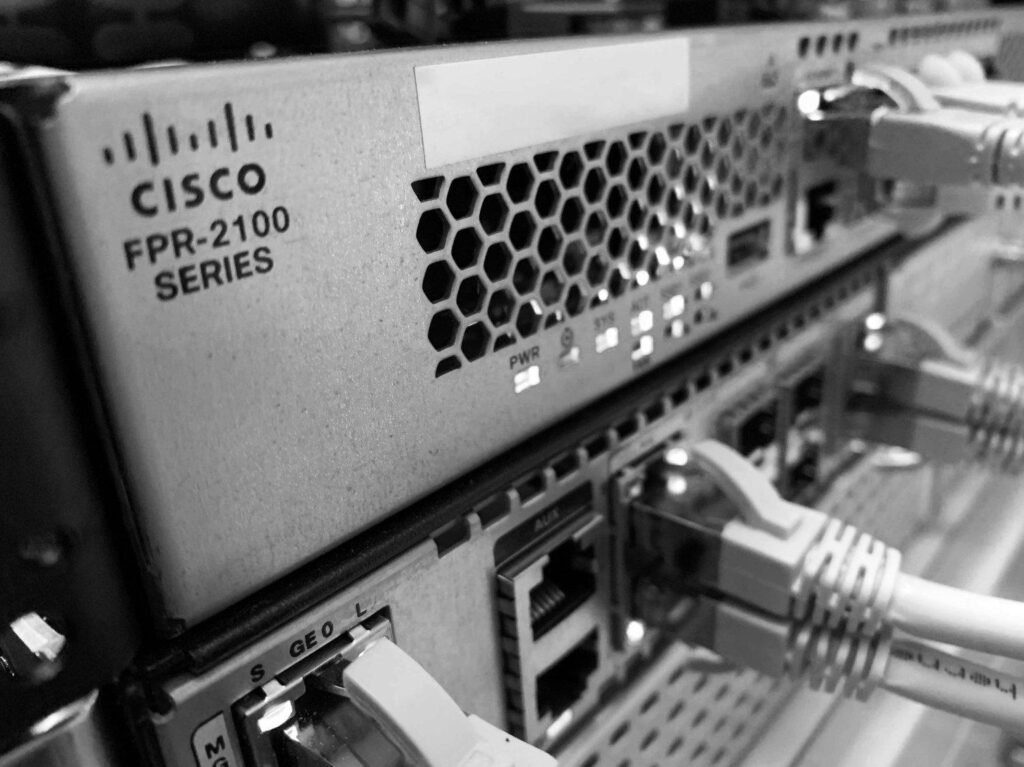
A high-severity vulnerability in Check Point security gateways has been exploited in real-world attacks, allowing hackers to escalate privileges to root. The company has released emergency fixes and urged customers to investigate their systems for signs of compromise.
Cybersecurity teams are facing another urgent security warning after Check Point disclosed that attackers have been exploiting a zero-day vulnerability in its security gateway products.
The flaw, tracked as CVE-2026-123039, allows an authenticated local user to execute commands with root-level privileges under certain conditions. Check Point says it observed active exploitation affecting a couple of dozen customers.
The attacks reportedly began in late October and involved multiple stages, including initial access through exposed Mobile Access portals, privilege escalation, persistence mechanisms and, in some cases, movement towards VMware ESXi infrastructure.
The disclosure is particularly important for organisations that rely on Check Point appliances to protect corporate networks and remote access services.
What is CVE-2026-123039?
The vulnerability affects the DynamicCLI inter-process communication interface used by the Gaia operating system on Check Point products.
According to the technical explanation reported by BleepingComputer, the DynamicCLI daemon runs with root privileges and listens on a local socket that does not properly authenticate connecting processes.
An authenticated local user could therefore send commands through that interface and have them executed with root-level permissions.
Root access is one of the highest levels of control on a Linux-based system. An attacker who obtains it may be able to modify system files, install persistent malware, access sensitive information and interfere with security controls.
The vulnerability is classified as a local privilege-escalation issue. This distinction matters: it does not mean that any internet user can automatically exploit the flaw without first obtaining a suitable foothold on the affected system.
Which Check Point products are affected?
The products identified in the reporting include:
- Check Point Firewall
- Multi-Domain Security Management Server
- Scalable Platforms
- Security Gateway
- Security Management Server
Organisations should consult Check Point’s official advisory to confirm whether their specific product versions and configurations are affected.
The company has released emergency hotfixes to address the vulnerability.
How attackers used the vulnerability

Check Point described an attack chain in which threat actors first gained access through Mobile Access portals by exploiting separate PHP2Shell vulnerabilities.
After obtaining an initial foothold, attackers used CVE-2026-123039 to escalate privileges to root.
The subsequent activity reportedly included deploying webshells and malware, establishing persistence and moving from compromised security gateways towards VMware ESXi infrastructure.
Check Point also reported destructive activity involving wiper malware in an investigated attack chain. A wiper is malicious software designed to destroy data or make systems unusable.
This illustrates why a vulnerability in a security appliance can be particularly serious: such devices often sit at the boundary between an organisation’s internal network and the outside world.
What organisations should do now
Check Point recommends applying the relevant emergency hotfixes as soon as possible.
Organisations that cannot immediately deploy the fixes should follow the vendor’s temporary mitigation guidance. BleepingComputer reports that Check Point advised stopping the dynamic_server process and preventing it from restarting as a temporary measure.
Security teams should also review their systems for indicators of compromise.
The vendor has published indicators and investigative guidance, including suspicious commands and unusual use of the system() function. Administrators should follow the official Check Point instructions rather than relying on a generic cleanup procedure.
A patch alone may not be sufficient if an attacker has already established persistence. Systems showing evidence of compromise may require forensic investigation, credential rotation and a carefully planned recovery process.
CISA adds the vulnerability to its exploited-flaws catalogue
The US Cybersecurity and Infrastructure Security Agency added CVE-2026-123039 to its Known Exploited Vulnerabilities catalogue on November 13.
The listing is significant because it confirms that the vulnerability is considered actively exploited in the wild.
For US federal civilian agencies, November 16 is the remediation deadline associated with the listing.
Although that deadline applies to the relevant federal agencies, other organisations using affected Check Point products should treat the issue as urgent because exploitation has already been reported.
Why this matters beyond Check Point customers
Firewalls and security gateways are designed to protect organisations from external threats. When attackers compromise the devices responsible for enforcing network security, they may gain a strategic position from which to target other systems.
The incident also highlights a broader cybersecurity lesson: perimeter security appliances need the same disciplined patching, monitoring and incident-response processes as servers, endpoints and cloud infrastructure.
For businesses, the priority is clear: identify exposed Check Point systems, install the vendor’s fixes, review available indicators and investigate any signs that an attacker may already have gained access.
Sources: Check Point security advisory and research; BleepingComputer reporting, November 13, 2026; CISA Known Exploited Vulnerabilities catalogue.