
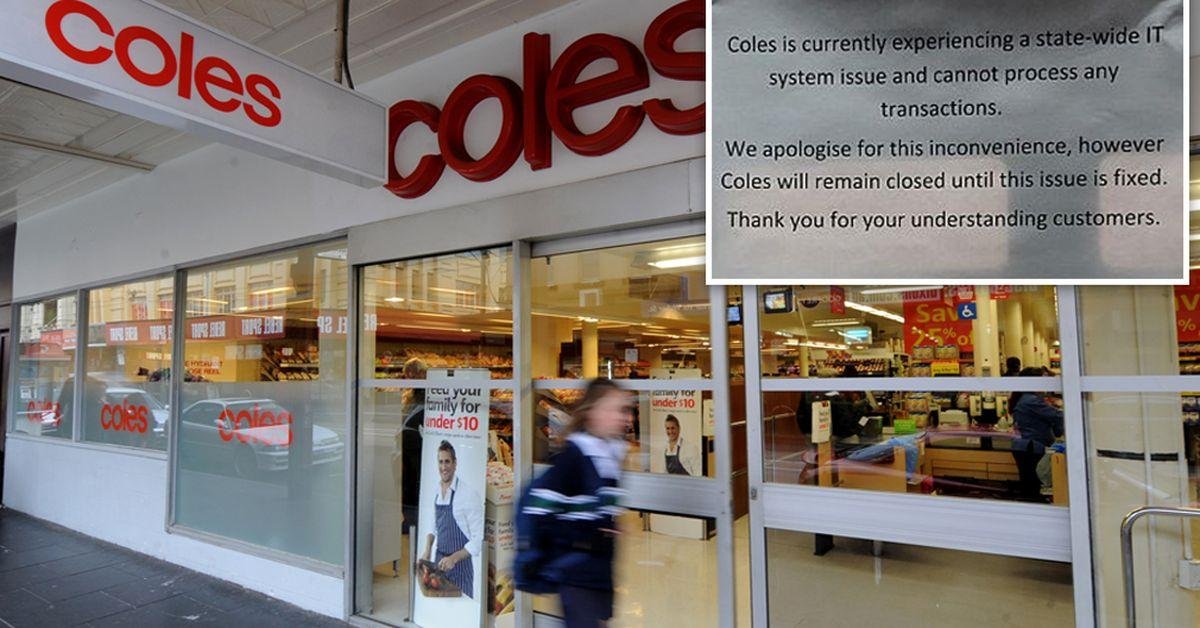
Australian supermarket giant Coles is investigating a cybersecurity incident and working with national authorities and external security specialists. The company says its investigation has not found evidence that customer, employee or supplier data was compromised or removed.
Coles Group has disclosed a cybersecurity incident affecting its IT environment, prompting an investigation involving the Australian Cyber Security Centre and external cybersecurity specialists.
In a statement released to the Australian Securities Exchange on November 16, the retailer said it had not identified evidence that customer, employee or supplier information had been compromised or removed from its systems.
The company has not publicly explained how the incident occurred, which systems were affected or whether attackers gained access to any part of its network.
What Coles has confirmed
The company said it is working with the Australian Cyber Security Centre and global cybersecurity experts to investigate the incident and contain any potential threat.
Coles also confirmed that its retail operations continue. Customers can shop in physical stores and through its online services as normal.
The company has not disclosed whether the incident involved ransomware, unauthorised access, malware or another type of cyber activity. It would therefore be premature to describe the event as a confirmed data breach or to attribute it to a particular threat group.
The distinction matters: a cybersecurity incident can involve suspicious activity or an attempted intrusion without necessarily resulting in confirmed data theft.
Are customer accounts and payment information affected?
At the time of its initial announcement, Coles said it had found no evidence of customer, employee or supplier data being compromised or removed.
That is a statement about the findings available during the investigation, not proof that no information was ever exposed. The company has not published a complete technical account of the incident.
Australian media reports also noted that Coles was looking into a small number of customer issues involving Liquorland click-and-collect services. The retailer had not established that these issues were connected to the cybersecurity incident.
Customers should rely on updates from Coles rather than assume that every service disruption is evidence of a data breach.
Why the incident matters
Large retailers hold and process substantial amounts of information across online shopping, loyalty programmes, payments, supply chains and employee systems.
Even when a cyber incident does not result in confirmed data theft, it can require extensive work to investigate affected systems, secure accounts and restore confidence.
Retailers are also attractive targets because disruptions can affect large numbers of customers and business partners. A successful intrusion may create opportunities for fraud, extortion or access to connected suppliers.
Coles has not confirmed that any of those outcomes occurred in this case.
What should customers do?
Coles has not announced that customers need to stop shopping or take emergency action. Its stores and online operations remain available.
Nevertheless, customers can take sensible precautions while the investigation continues:
- Use a strong, unique password for their Coles account.
- Avoid reusing that password on other websites.
- Be cautious with unexpected emails, text messages or phone calls claiming to come from Coles.
- Do not open suspicious links or provide passwords and verification codes in response to unsolicited messages.
- Check account activity and report transactions or changes they do not recognise.
These are general security precautions, not evidence that Coles accounts have been compromised.
Coles said it will provide further updates as appropriate while it works with the relevant authorities and security specialists. The most important unanswered questions concern the nature of the incident, the systems involved and whether the investigation eventually identifies any unauthorised access or data exposure. For now, the company’s public position remains limited: a cybersecurity incident is under investigation, no evidence of customer, employee or supplier data compromise has been identified so far, and normal retail operations continue.
The findings of the ongoing investigation will determine whether further customer notifications or security measures are necessary.